IMPLEMENTED IN DEVELOPMENT
Content-addressed storage
Chunking, hashing, verification and object lifecycles have implementation evidence. Local file access is separate from distributed storage; durable multi-provider availability is not guaranteed.
Global Neural System
A network where participating devices can exchange content and coordinate work, with a history that can be checked.
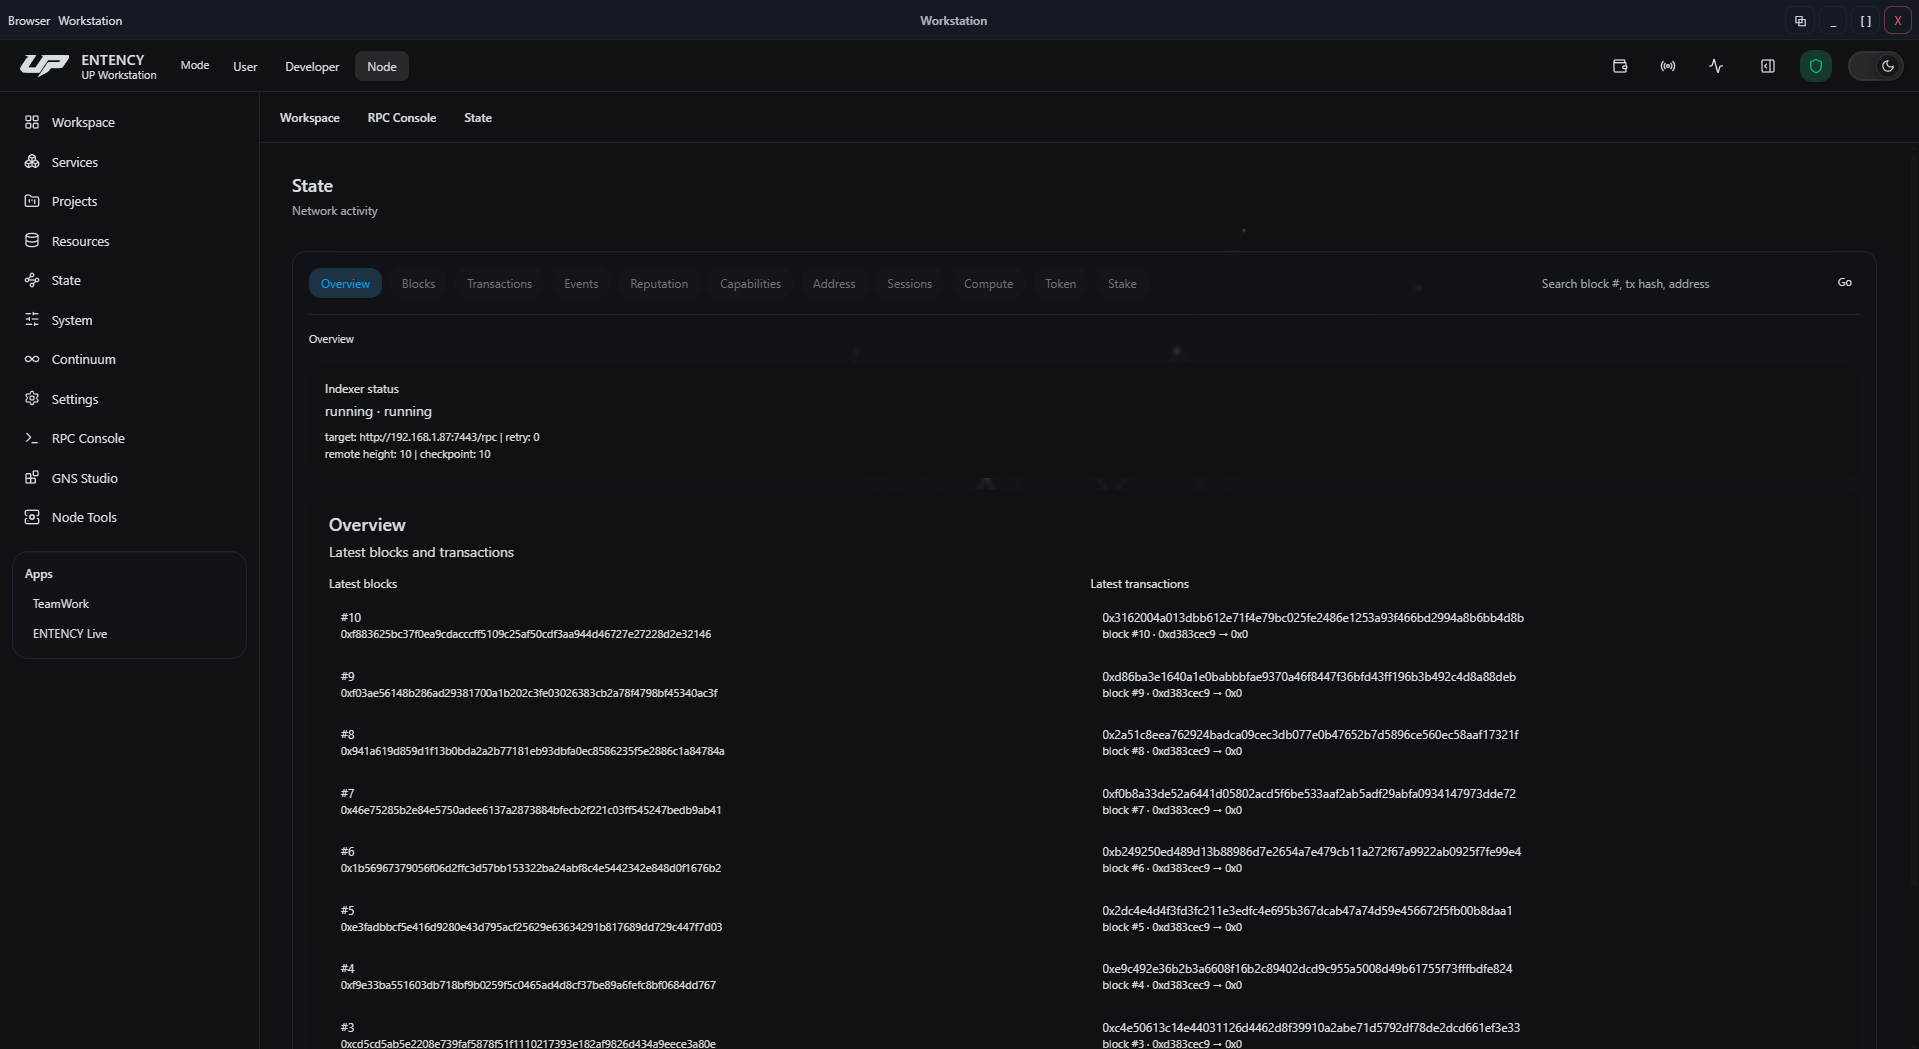
GNS can preserve the history of supported network state. This makes changes inspectable without claiming to record every user action or keep every file forever.
A node keeps track of supported network changes, stores and checks content, finds other nodes and exposes tools for inspecting what happened. What it can provide depends on its capabilities and configuration.
A new node starts with known contact points, then can learn about more nodes through the ones it meets. Saved contacts can help after a restart, but a saved address is never proof that a connection still works.
IMPLEMENTED IN DEVELOPMENT
Chunking, hashing, verification and object lifecycles have implementation evidence. Local file access is separate from distributed storage; durable multi-provider availability is not guaranteed.
FOUNDATION
Supported communication workflows include receiver acknowledgements and Studio app examples. An acknowledgement is runtime acceptance, not cryptographic verification or chain finality. General reliable messaging is still in development.
IMPLEMENTED IN DEVELOPMENT
Compute jobs, signed votes and quorum rules let supported results be checked by participating nodes. This is a bounded implementation, not an open compute marketplace or evidence of sector workloads.
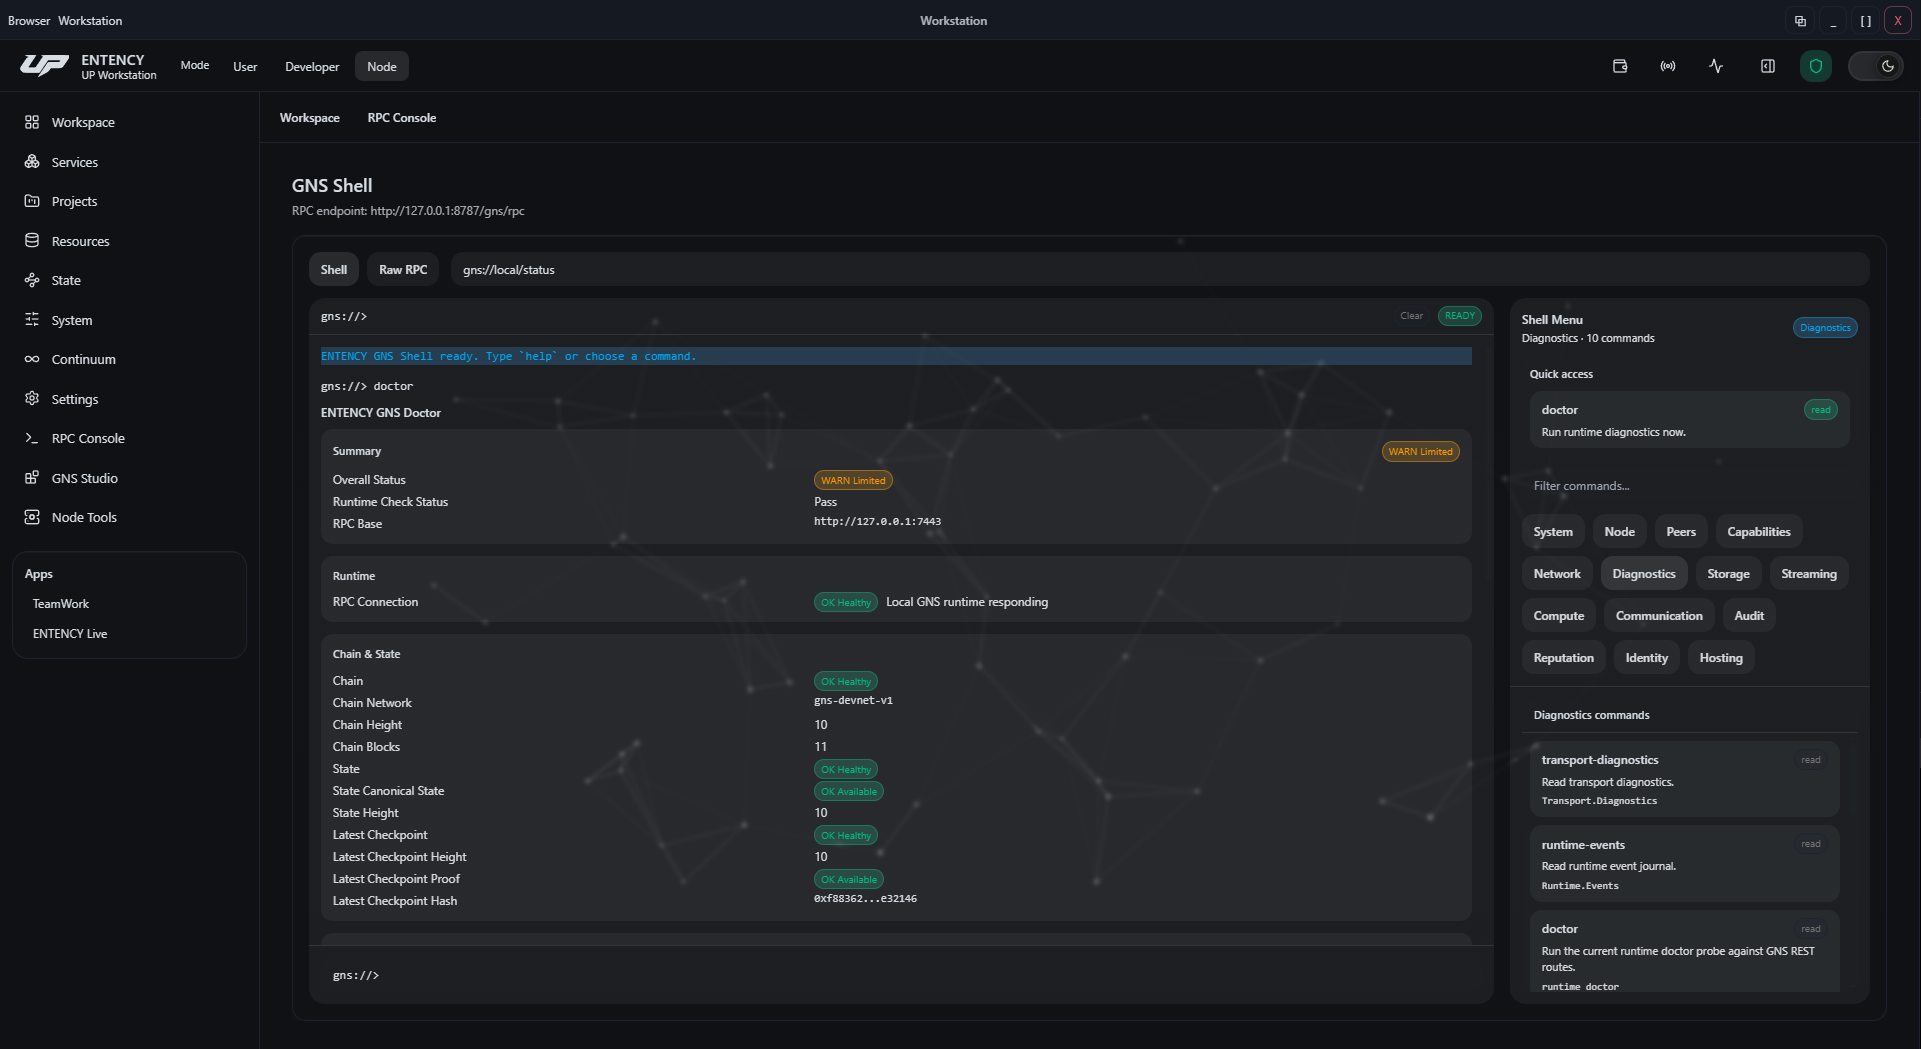
The peer network uses discovery hints, a peerbook, expiring peer announcements, and minimum/maximum peer policies. Framed hello, header/block exchange, gossip, and anti-entropy synchronization have development evidence. The exercised framed carrier is HTTP; final internal TCP+TLS transport parity is not established.
Nodes can combine configured seeds, constrained bootstrap descriptors, learned peers and cached discovery hints. A controlled LAN lab demonstrated first entry and source recovery. Cached hints expire and must pass the peer handshake again after restart. The bundled production descriptor list is empty; a public bootstrap fleet is not established.
UPnP and NAT-PMP code attempts router mappings, renewal and cleanup. Observing an address or receiving a router acknowledgement does not prove that another Internet host can reach it. The recorded real-router attempt did not obtain a public mapping; broad router and remote acceptance remain unverified.
Controlled PC and Android labs exercised relay candidates, reservations and a relayed path through a helper. This is stronger than a design-only foundation, but does not establish a public relay fleet or universal NAT traversal. A relay requirement, an available path, an active route and an accepted peer connection remain separate facts. Anchor forwarding is not established.
Transport NodeID is separate from producer/wallet identity. The current peer handshake checks identity consistency but does not prove possession of the advertised transport key: connected routes remain identity-claim-only, not authenticated peers. Transport encryption and public-network security must not be inferred from connectivity or TLS configuration labels.
Canonical capabilities support signed grants, revocation, and delegation with narrower actions, scope, and depth. Reputation is bounded and derived from canonical events. Peer scoring, rate limits, content verification, and reorganization guards provide implemented hardening; they do not close the full production security model.
Application and service registries bind identity, namespace, runtime-package, and schema references. Hosting foundations add publication revisions, object/chunk asset bindings, provider capability checks, freshness, and replica-fallback plans, audit traces, and operator readiness gates. Registering a service does not execute it; these contracts do not prove live multi-provider publishing, retrieval, or replication.
Hash-addressed objects and application/service namespaces provide addressing foundations. Hosting route identities are modeled, but public DNS and zero-configuration public hosting are not complete. Predictive cache/prefetch/routing evidence is deterministic and fixture-backed, not production adaptive AI routing.
Node diagnostics expose configuration, peers, bootstrap, reachability, NAT/relay limits, and transport state through CLI and query interfaces. The explorer rebuilds read models from canonical state and events; its views are not independent authority.
ENT is the network fuel/token terminology. Contribution records and accounting foundations model reserves, fee debits, and reward credits. This does not establish complete token economics, production reward correctness, exchange functionality, or an available public token service.
Reviewed against the current development source on 21 October 2026. Implemented features are not a production release. Controlled-lab results and public Internet operation are reported separately.
Compute jobs, signed votes and quorum rules let supported results be checked by participating nodes. This is a bounded implementation, not an open compute marketplace or evidence of sector workloads.
App/service registries, publication revisions and storage bindings exist as building blocks. Complete public hosting and live multi-provider replication are not established.
Still to validate: production bootstrap infrastructure and broad Internet connectivity. Controlled LAN bootstrap and PC–Android relay results do not establish a public network. ENT accounting and resource contribution remain limited foundations; AXI is planned.
Start with the Litepaper for the ecosystem model and current direction. The Technical Whitepaper destination explains the planned technical coverage and its publication status.
Read the available introduction to GNS, UP, identity, and the relationship between the components.
READ THE LITEPAPER →Detailed protocols, security and implementation documentation are not yet published. Follow the existing documentation page for its status.
VIEW DOCUMENTATION STATUS →There is no public node package linked here yet. Development updates and future test-access announcements are available through the existing Early Access section. This page will become a starting point for verified node releases when they are published.